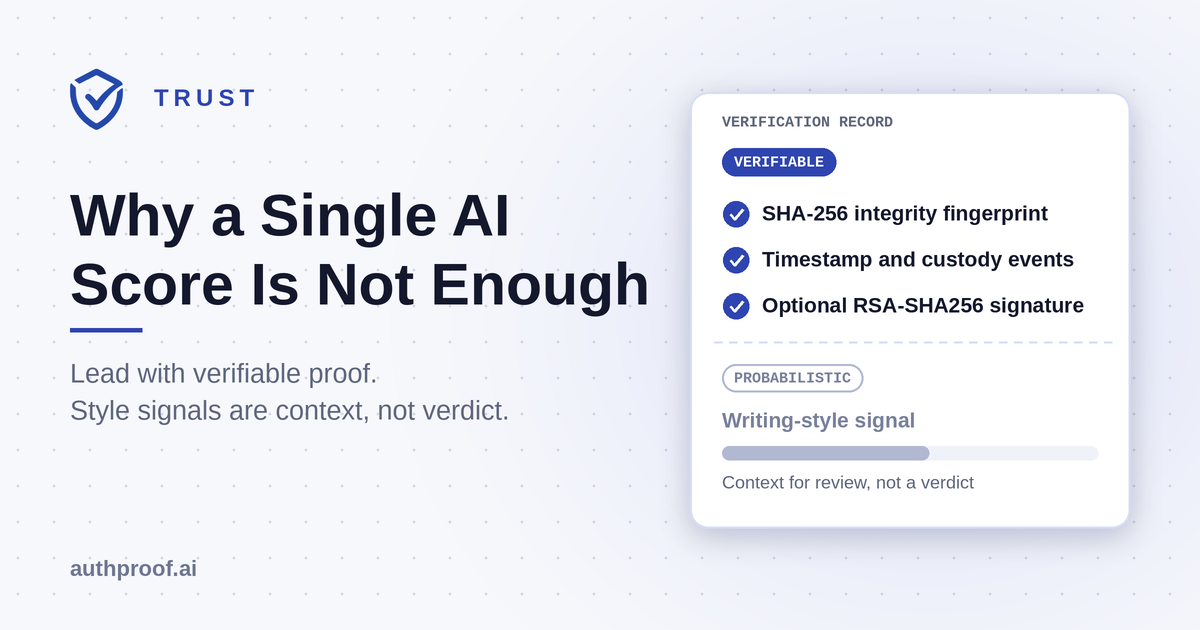
When a writing-style classifier flags human content as machine-generated, consequences follow: disputed submissions, editorial rejections, and reputational damage. For organizations building trust infrastructure, the lesson is not to hide uncertainty - it is to architect workflows so cryptographic integrity proof leads and every probabilistic signal is labeled, bounded, and reviewable by a human reviewer.
Why false positives happen
Classifiers trained on narrow human baselines over-flag clear, structured prose - including strong professional writers and many non-native English authors. As generative models evolve, statistical boundaries shift. A single headline score creates false precision: “87% likely AI-generated” still implies material error rates when you operate at scale. Policies built on a single probabilistic score invite legal and operational exposure.
Lead with what is verifiable
SHA-256 fingerprints prove the exact bytes registered at submission. Timestamps and chain-of-custody events show what happened after upload - analysis, signing, report generation. Optional Ed25519 signatures bind records to your signing key. Those claims are independently testable. Writing-style likelihood is not; it belongs in a separate lane on the verification report, never as a silent gate.
Use analysis as context, not verdict
AuthProof attaches duplicate registry checks and optional writing-style signals to the same proof record - always marked supplementary and probabilistic. Borderline cases should route to human review with PDF reports and public verification links, not automated rejection. Team leads need language they can defend to readers and auditors; security teams need artifacts, not black boxes.
Policy patterns that scale
Publish a written standard: what you prove cryptographically, what you merely suggest, and who decides edge cases. Train reviewers on verification certificates before they interpret scores. Retain signed reports for audit. When procurement asks for “AI analysis,” redirect the conversation to integrity evidence plus transparent supplemental analysis - that is the enterprise-grade answer AuthProof is built to support.