Threat models for digital content expanded beyond deepfakes and spam generation. Teams now face hybrid human-AI edits, hidden instructions embedded in submissions, swapped files after approval, and spoofed provenance claims in review queues. Analyzing only the finished document ignores how it was produced and whether it changed after a trusted checkpoint - exactly where high-trust workflows break.
Why detection-only defenses fail
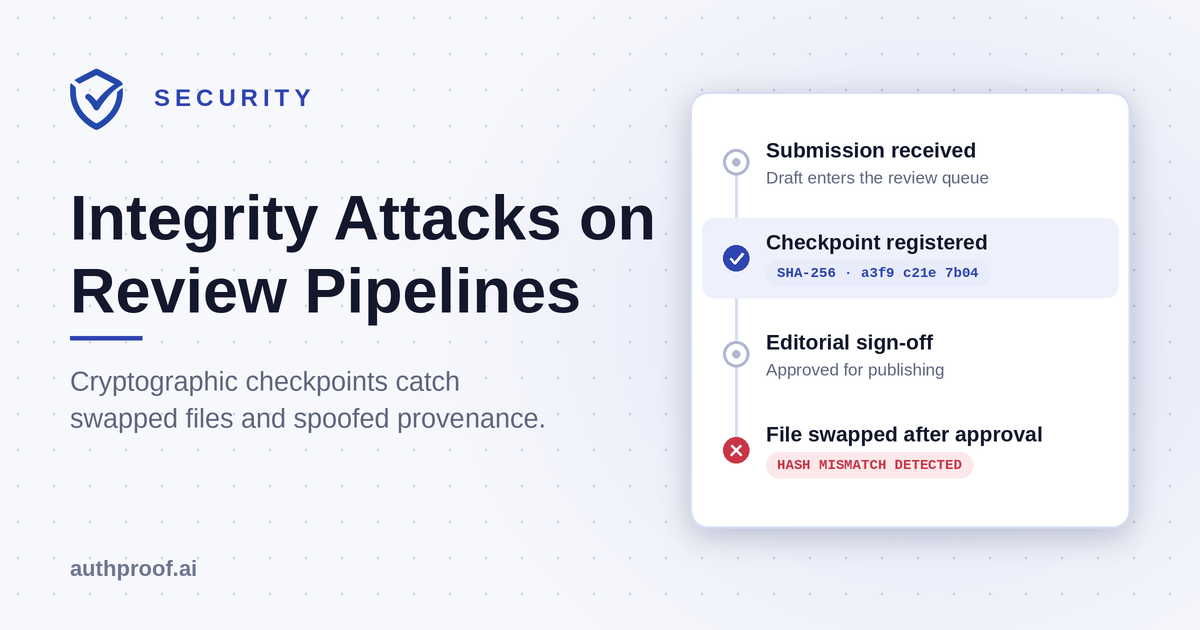
Post-hoc classifiers can be evaded with light paraphrasing, structural edits, or re-export from another tool. Prompt-injection style attacks target systems that treat untrusted text as instructions. A durable control is to register content at a defined workflow step - creating a tamper-evident record before downstream manipulation matters for your policy.
Checkpoints your security team can audit
SHA-256 integrity hashing answers a simple question: does this file still match what we registered? Optional Ed25519 signatures tie records to your keys. Duplicate registry checks surface prior submissions of similar content. Signed PDF verification reports and public verification pages give security and editorial teams artifacts they can hand to auditors - not opaque scores locked in a vendor UI.
Defense in depth
Combine integrity hashing, optional signatures, registry signals, and transparent verification certificates. Defeating one layer should not collapse the entire trust story. Process controls still matter - least privilege on signing keys, retention policies, revocation of public links when content is withdrawn - but cryptography gives you a shared evidentiary language across departments.
Run a tabletop exercise
Walk through one incident: a file swapped after editorial sign-off, or a submission altered after a checkpoint. Identify where a proof record would have created a verifiable checkpoint. Pilot AuthProof on that step, export a sample report, and validate whether legal and IT agree on proof scope. That exercise beats another generic “AI security” slide deck.