Content provenance - a verifiable record of where an asset came from, how it was created, and whether it has been altered - is moving from research slides to production requirements. The Coalition for Content Provenance and Authenticity (C2PA) and the Content Authenticity Initiative (CAI) define open specifications for attaching cryptographically signed metadata to digital assets. For publishers and platforms, the question is no longer whether provenance matters, but how to operationalize it across file types your teams actually handle.
What C2PA actually proves
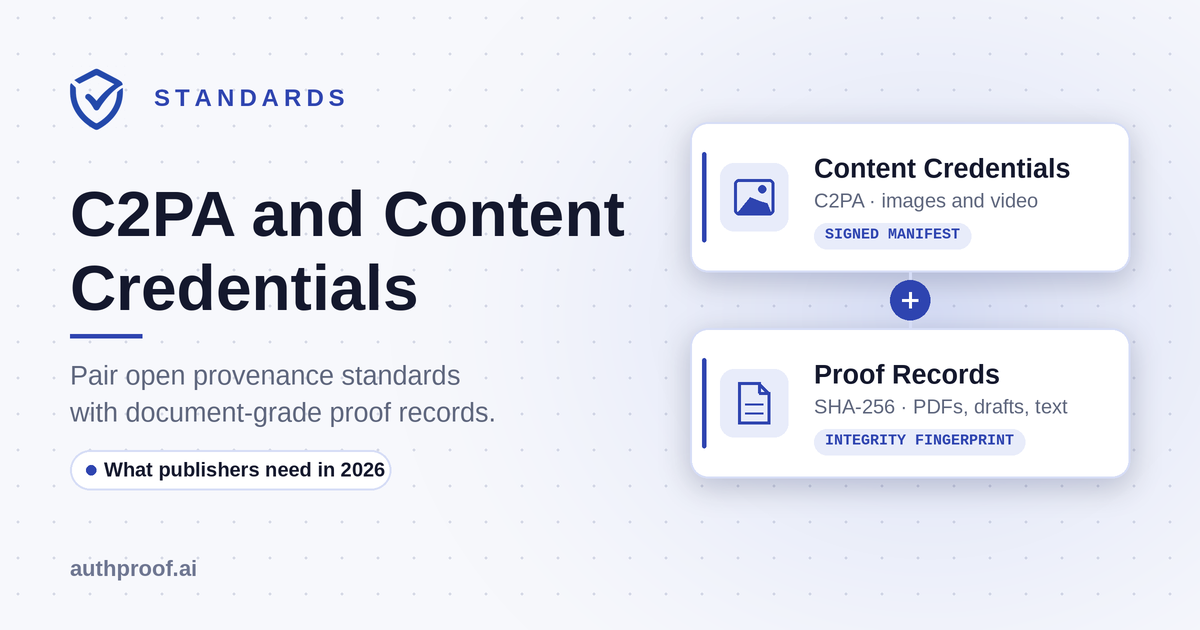
C2PA defines Content Credentials: signed manifests that bind assets to origin information (creator, tools, timestamps) using public-key infrastructure. Adoption is strongest in camera and platform image and video pipelines, but the specification itself has expanded. C2PA 2.2 adds manifest embedding for PDF 1.7 and 2.0, along with trusted timestamps and identity assertions - so document-grade credentials are part of the standard, not a future hypothetical.
Intake boundaries and legacy content
Spec support is not the same as universal deployment. High-trust workflows still ingest legacy PDFs, drafts, plain-text submissions, and user uploads that never passed through a C2PA-aware export or signing toolchain. Newsroom archives, submitted documents, and internal reports often arrive without embedded credentials even when your policy requires proof today. AuthProof registers SHA-256 integrity fingerprints, optional Ed25519 signatures, and chain-of-custody timelines so organizations can issue shareable verification certificates at ingestion when upstream metadata is missing or incomplete.
Standards plus workflow proof
Mature enterprise programs treat C2PA and hash-based proof as complementary layers. Credentials attached at capture or export protect downstream rich media. Proof records at ingestion protect documents at the boundary where your policy applies. Public verification links let third parties validate integrity without access to your CMS or LMS. Neither layer alone covers every channel; together they reduce blind spots.
Honest scope still matters
Neither C2PA nor SHA-256 proof automatically verifies that every factual claim in content is true. They establish cryptographic evidence about the artifact and its history. Pair standards-aligned provenance with transparent verification pages that state what is proven and what is not - that is how durable reader and regulator trust is built.
What to do now
Document provenance requirements per workflow: publishable media, source documents, and registered submissions. Pilot one path end-to-end: register proof at intake, sign when policy requires, publish verification for external audiences. Measure time-to-verify for auditors and readers, not slide count. That is the fastest path from standards awareness to operational trust.